
To bring a high level of expertise on-board IAFs increasingly include persons that are not trained as auditor and/or have no experience in performing internal audits. These non-traditional auditors, often named rotational auditors, guest auditors or ‘subject matter experts’, function as part of the IAF for a specific period of time and come from within the organization or are hired from the outside. The use of non-traditional auditors has several advantages for the non-traditional auditors themselves, the IAF and the organization. The purpose of this document is to share better practices regarding the use of non-traditional auditors in the IAF. These real-life examples are recommended protocols put in place to profit from the advantages of using non-traditional auditors, to ensure their valuable inputs contribute to the objectives of the audit function without compromising the quality of the audit process and its outputs. You can read the comprehensive overview here

Vaktechnische Publicaties
In ons kenniscentrum vindt u een uitgebreide verzameling vaktechnische publicaties die u ondersteunen bij uw werkzaamheden als internal auditor. Van praktische handleidingen en whitepapers tot diepgaande analyses en internationale standaarden – al onze publicaties zijn gericht op het versterken van uw expertise en het verhogen van de kwaliteit van interne audits. Ontdek waardevolle inzichten en blijf up-to-date in het dynamische vakgebied van internal auditing!
Zoekt u een specifieke publicatie? Gebruik de zoekbalk bovenaan de pagina.
Gebruikt u een mobiel apparaat? Open dan het menu (☰) om de zoekfunctie te vinden.
Without question, 2020 was defined by the global coronavirus pandemic (GCP). By March, as the research for Risk in Focus got underway, Europe had become the epicentre of the biggest public health crisis in living memory. This caught most countries and businesses off guard, despite the fact the World Economic Forum and others had already been sounding the alarm on global health security and the probability of a pandemic event. Not only has the virus had huge public health consequences, social distancing and lockdown measures have had profound economic impacts. The GCP is the most significant and far-reaching event for businesses since at least the global financial crisis of 2008, and is expected to cause a deeper recession, higher rates of unemployment and bigger increases in public debt. Businesses and their risk profiles have been significantly affected by coronavirus. The safety of workers has been a priority, with staff sent home to work in the first half of 2020 under orders from governments and employers. Lockdowns inevitably caused immense operational disruption as companies were forced to rapidly adjust and sectors including manufacturing, construction and industrials had to reduce output in order to maintain distancing measures within their core business. The beginning of summer 2020 was marked by an easing of restrictions as governments managed the delicate balance of kickstarting their economies with resurgences in infections. It is expected that this challenge will have to be managed throughout 2021. Although the exact course of the pandemic’s development is uncertain, it was continuing to accelerate in the second half of 2020. The longer-term implications of this exceptional scenario are less clear. Lessons will be learned over the coming months and years by governments and businesses. Internal audit can and should assist in this regard. Its unique 360-degree view of the business and risk-control mindset can help organisations identify their blind spots and opportunities to improve their operations. Looking ahead to 2021, internal audit’s enterprise-wide perspective has never been more necessary. Boards and executive management teams will depend on this independent top-down viewpoint for insights into the business and its risks during what remains a significantly challenging period. This is the exceptional backdrop against which this year’s Risk in Focus is set. Also available: Board briefing Guidance Cybersecurity and data security Webinar Cyber and Data Security Guidance Macroeconomic and geopolitical uncertainty Guidance Climate change and environmental sustainability
Putting risk into focus for the board Board members must be aware of their organisations’ principal risks (and opportunities) and the external threats to their operations and strategies. They should also have confidence that internal audit is prioritising these. Especially now. The risk landscape has taken a dramatic and unexpected turn. Looking ahead to 2021 we see that the global coronavirus pandemic (GCP) is likely to shape the risk profiles of organisations in many ways. Rather than posing a novel risk, the pandemic has exacerbated and magnified existing risks as well as opportunities that you as a board member should be mindful of. This briefing summarises insights from the latest edition of our annual report, Risk in Focus 2021 (RiF21), which this year is a collaborative project between ten institutes of internal auditors from across Europe.
The internal audit function has an important role to play in providing assurance over the effectiveness and security of key processes outsourced from (re)insurance undertakings to third parties. It is crucial that key stakeholders, including management, the board and the (re)insurance undertaking’s supervisors can place reliance on the work of internal audit in respect of the risk management of third parties, while at the same time maintaining a reasonable expectation of the extent of the internal audit function’s responsibilities in this area. This paper sets out the view of the ECIIA Insurance Committee (the Committee). It is based on the position paper on Internal Audit Oversight of external outsourcing issued by the ECIIA Banking Committee, on best practices that could be adopted by internal audit functions in respect of the audit of externally outsourced services. This paper was adapted to the specifics of the (re)insurance undertakings, in particular the regulatory requirements of Solvency II. This paper does not consider: Outsourcing of internal audit as a function Internal outsourcing (from one legal entity to another within the same group), albeit many of the same concepts could be applied
Internal Auditing Around the World, Volume 16 - The future auditor had arrivedThe future auditor has arrived. It’s a bold statement — and it’s true. The future auditor is a vision, inspired partly by the definition of internal auditing from The Institute of Internal Auditors: ‘‘an independent, objective assurance and consulting activity designed to add value and improve an organization’s operations.’’ When Protiviti first articulated this vision in 2014, we explained that the future auditor, once personified, would be recognized as a ‘‘positive change agent’’ in the organization. We also asserted that chief audit executives (CAEs) who embraced this vision would be ‘‘better positioned to demonstrate to executive management and the board the value contributed by internal audit through their comprehensive risk focus and forward-looking, change-oriented and highly adaptive behavior.’’ Six years later, we see that many internal audit leaders around the globe have answered that call to action — and are committed to bringing forth a next-generation internal audit function. They, and their teams, have disrupted their function’s status quo by thinking differently about how internal audit performs its work and delivers results that do, in fact, add value to the business.
This Global Perspectives and Insights describes the Internal Audit Ambition Model from the perspective of several CAEs who have applied it. Looking toward to its potential applications, the report considers how the model may be used as part of the internal audit activity’s quality assurance and improvement program (QAIP). In today’s unprecedented and volatile business environment, organizations face a future that is as difficult to predict as it is open for creativity and innovation. The internal audit activity can play a vital role in helping organizations anticipate, evaluate, and respond to risks and opportunities. And CAEs must effectively demonstrate that value. CAEs need robust tools to continuously enhance the value that the internal audit activity provides to management and the board. Perhaps equally important, the right tool should enrich the ability to clearly express internal audit’s potential. The Internal Audit Ambition Model seeks to help CAEs achieve those goals. The Internal Audit Ambition Model may help the internal audit activity: Adopt a common approach and consistent criteria for conducting self-assessments of its current (“achieved”) quality. Help drive conformance with the The IIA’s International Professional Practices Framework. Establish a peer benchmark against which to compare itself. Create a visualization of its achievements in key process areas. Identify the “ambition” level to which it aspires. Identify gaps that must be filled to achieve its desired ambition level. Communicate with senior management and the board about its achieved level of quality and its level of ambition. According to the model’s authors, the word “ambition,” distinguishes this model from maturity models because it communicates the CAE’s choice about the level to which the internal audit activity should aspire. The choice takes into account the input of senior management and the board in light of factors such as the complexity of the organization, the size of the internal audit activity, and the industry in which the organization operates. The word “ambition” moves the focus from simply meeting the requirements to inspiring intentionally chosen improvements.
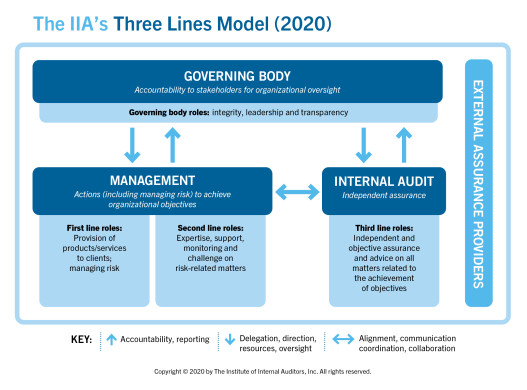
This paper offers a practical approach to directly address the scenario of an increased risk of fraud (corruption, misappropriation of assets, fraudulent financial statements) in organizations due to the pandemic. It considers related key actions, including assessment of vulnerabilities, risk mitigation, and monitoring fraud alerts (red flags). This report also presents a useful analysis on how to face a possible increase in the risk of fraud in these times of COVID-19 (pre- and post-pandemic) from the perspectives of the fraud triangle, the Three Lines of Defense model, cybersecurity, and global risk. People and organizations around the world are fighting to overcome the crisis caused by the COVID-19 pandemic and its direct and collateral effects. In this fight, internal auditors are actively helping organizations overcome and recover from the crisis. Download it today and watch Continuing the Conversation for a deeper dive.
Information technology is a fundamental part of all organizations, so internal auditors should have a fundamental understanding of their organization’s IT functions and processes. Because IT is imperative to business strategy, understanding the impact technology can have on business processes and making accurate and timely recommendations can elevate internal audit as a trusted advisor and value creator. This guidance will enable internal auditors to understand: The relationship between IT and the business. The various network structures, components, and related concepts. IT infrastructure, including hardware, software, and databases. How organizations use, implement, and develop applications. Relevant topics such as data analytics, social media, machine learning, RPA, and more. This is for members only. To access it and other valuable resources, become a member today.
Na de practice guide (PG) over Auditing Culture (eind 2019), is nu een specifieke PG verschenen over Auditing Conduct Risk. Zoals wordt aangegeven is ‘gedrag’ niet gemakkelijk te scheiden van de cultuur; gedrag kan worden gezien als de manifestatie van cultuur. Deze PG is vooral gericht op de financiële sector en op het evalueren van het management van het ‘conduct risk, ofwel het risico van wangedrag. Daarbij wordt uitgegaan van de ‘nalevingsstrategie’ (de organisatie vertelt duidelijk wat het gewenste gedrag is, bewaakt dat en sanctioneert bij overschrijdingen). Minder aandacht wordt besteed aan de zogenaamde ‘stimueringsstrategie’, gericht op het moreel redeneren door de medewerkers in lastige situaties (dilemma’s), zoals vaak ook onderdeel is van compliance- en integriteitsprogramma’s binnen organisaties. English The issue of conduct is not easily separated from an organization’s culture; rather, it is a distinct segment of culture as a whole. Internal auditors can add value by assessing and reporting on their organization’s conduct risk management. The internal audit activity can help drive strong internal control risk management frameworks (including conduct risk) that align with stakeholder expectations, supporting boards, audit committees, and executive management in their oversight roles. This guidance will enable internal auditors to understand: The business significance of conduct risk in an organization’s control environment. The key components of conduct risk. Key stakeholder (including regulator) concerns and expectations related to conduct risk. Internal audit’s role in assessing and reporting on organizational culture and management of conduct risk. An approach to assess and report on an organization’s culture and management of conduct risk. The eBook Practice Guide: Auditing Conduct Risk costs $25.00
In today’s unprecedented environment, effective internal auditing requires thorough planning coupled with nimble responsiveness to quickly changing risks. To add value and improve an organization’s effectiveness, internal audit priorities should align with the organization’s objectives and should address the risks with the greatest potential to affect the organization’s ability to achieve its goals. Ensuring alignment between internal audit priorities and the organization’s objectives is the essence of Standards 2010 – Planning, 2010.A1, 2010.A2, and 2010.C1, which task the chief audit executive (CAE) with the responsibility of developing a plan of internal audit engagements based on a risk assessment. This practice guide will help the CAE and internal auditors create and maintain a risk-based internal audit plan. The guide describes a systematic approach to: Understand the organization. Identify, assess, and prioritize risks. Coordinate with other providers. Estimate resources. Propose the plan and solicit feedback. Finalize and communicate the plan. Assess risks continuously. Update the plan and communicate updates. The eBook Practice Guide: Developing a Risk-based Internal Audit Plan costs $25.00
The first in a three-part series, this report serves as a how-to guide to assist internal auditors in assessing their current level of preparedness regarding privacy and data protection issues, particularly as their approaches relate to the present state of the profession overall. Further, the report is intended to help internal auditors understand specific risks and threats and to help them ensure that relevant controls are developed, implemented, and operated effectively. The framework, audit plan, and implementation discussions in the later sections of the report are designed to provide a foundation on how internal audit departments can build their own structures. You can find part 2 here.
De IAF heeft zich ontwikkeld tot een essentieel zintuig van de board, een voelspriet, een sonde die het topmanagement en de raad van commissarissen voortdurend belangrijke informatie geeft over de beheersing van de risico’s binnen de onderneming – risico’s die veel verder gaan dan de betrouwbaarheid van de financiële verantwoording of compliance met wet- en regelgeving, maar die ook betrekking hebben op de uitvoering van de strategie, het creëren van waarde op lange termijn en de continuïteit van de onderneming. Deze speciale uitgave omvat negen artikelen en twee prikkelende essays van auteurs die ruimschoots hun sporen binnen het vakgebied hebben verdiend. De eerste drie bijdragen beschouwen de IAF in zijn huidige context. Vervolgens gaan twee artikelen over de menselijke factor binnen de IAF. Hierna behandelen drie artikelen de actuele ontwikkelingen die de IAF doormaakt, zoals de betekenis van digitalisering en algoritmes en aansluitend twee bijdragen over de werkwijze van de IAF in de praktijk. Het themanummer sluit af met een prikkelend essay over de rol van de IAF in een complexe wereld waarin innovatie essentieel is om te overleven. De artikelen in deze speciale uitgave geven een caleidoscopisch beeld van de IAF dat elke MAB-lezer zal kunnen boeien. Daarnaast leveren zij een bijdrage aan de bestaande onderzoeksliteratuur en aan eventueel toekomstig onderzoek over dit onderwerp. Deze publicatie is tot stand gekomen in samenwerking met de Stichting Vaktechnisch Onderzoek van het Instituut van Internal Auditors Nederland. De redactie houdt zich uiteraard aanbevolen voor suggesties en opmerkingen naar aanleiding van dit bijzondere nummer van het MAB. Naar de online uitgave van het themanummer De internal auditfunctie van het MAB
Diversity is a broad and extremely timely topic in today’s environment. A conversation regarding diversity within an organization is worth having because significant research shows that it has a tangible impact on both workplace productivity and organizational value. In contrast, a lack of diversity is an organizational risk as relevant as any other risk worth being recognized by an internal audit activity. According to the International Professional Practices Framework (IPPF), it is internal audit’s mission “to enhance and protect organizational value by providing risk-based and objective assurance, advice, and insight.” This edition of Global Perspectives and Insights sheds lights on how diversity impacts the workplace and affects productivity and organizational value. It will also explain why internal audit should be an advocate for diversity in all its forms within both its own activity and the organization as a whole. This is for members only. To access it and other valuable resources, become a member today.